Packet sniffing from a mirror port, a TAP or inline, at 100 Gbps.
Packet Sensor is the component of Wanguard and Wansight that inspects IP packets — from SPAN or RSPAN port mirroring, a network TAP, or a server in the main data path — with libpcap, PF_RING, Netmap or DPDK, at 100 GbE and more than 30 million packets per second per instance. Five-second graphs, one-second detection, packet captures you read in a Wireshark-like page, and the same per-endpoint responses as the Flow Sensor.
Wanguard overviewFlows or packets?Sensor licenses
100 GbE · > 30 Mpps per instance · detects in ≤ 1 s · graphs every 5 s
What a Packet Sensor shows you
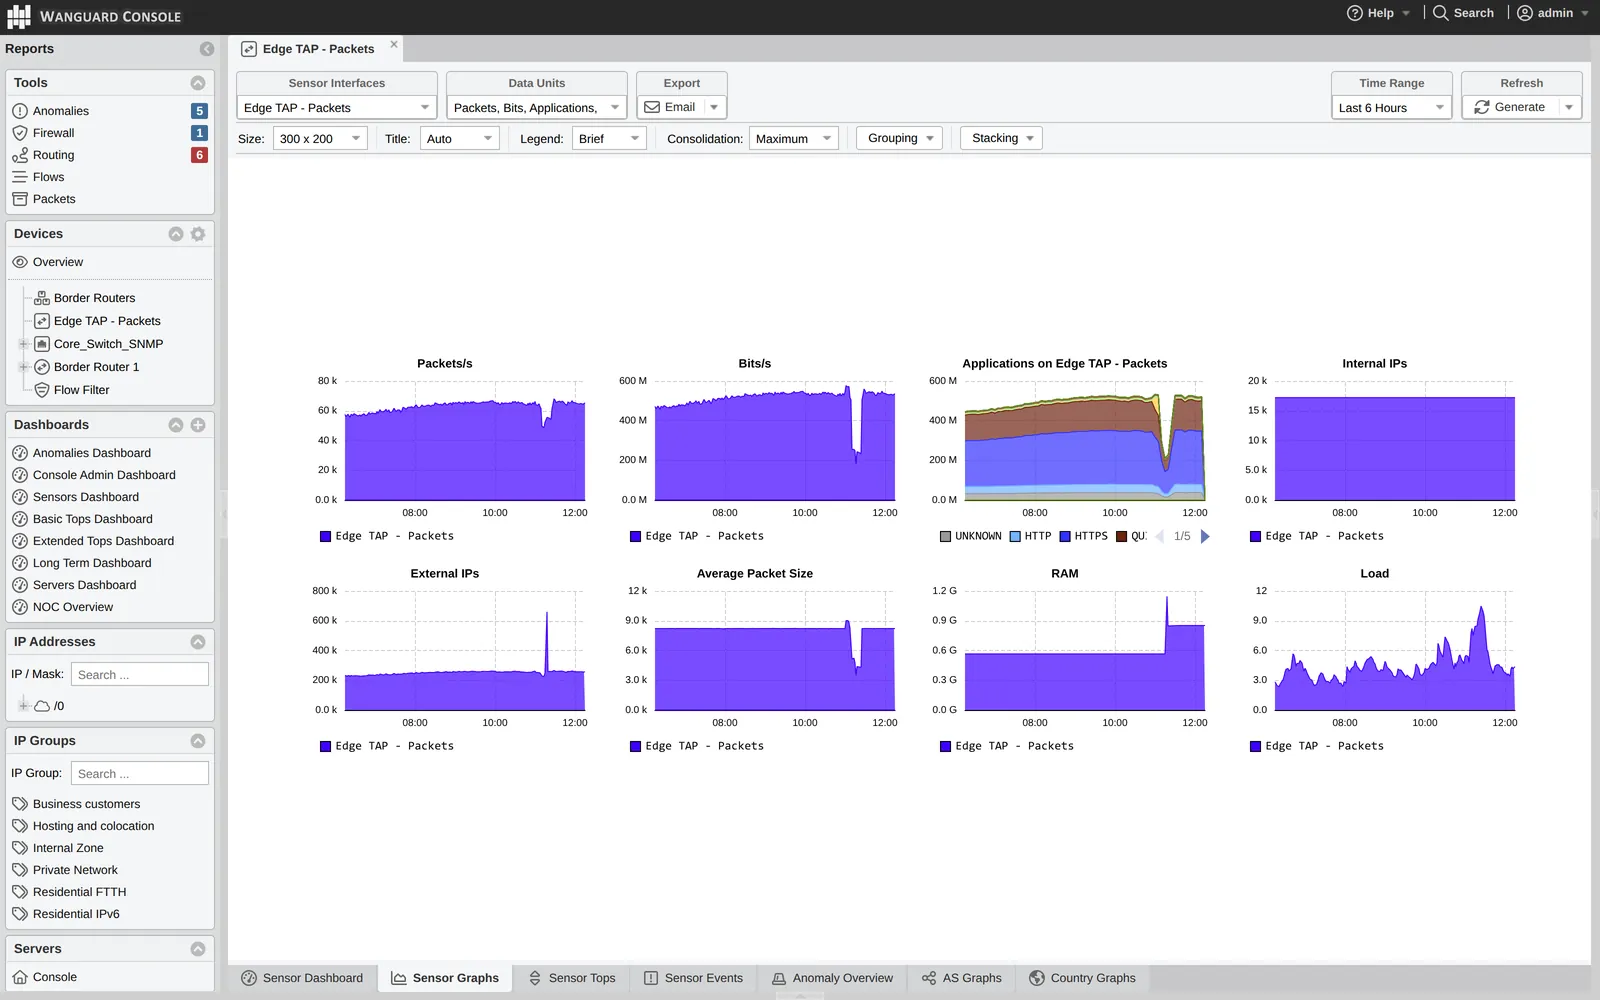
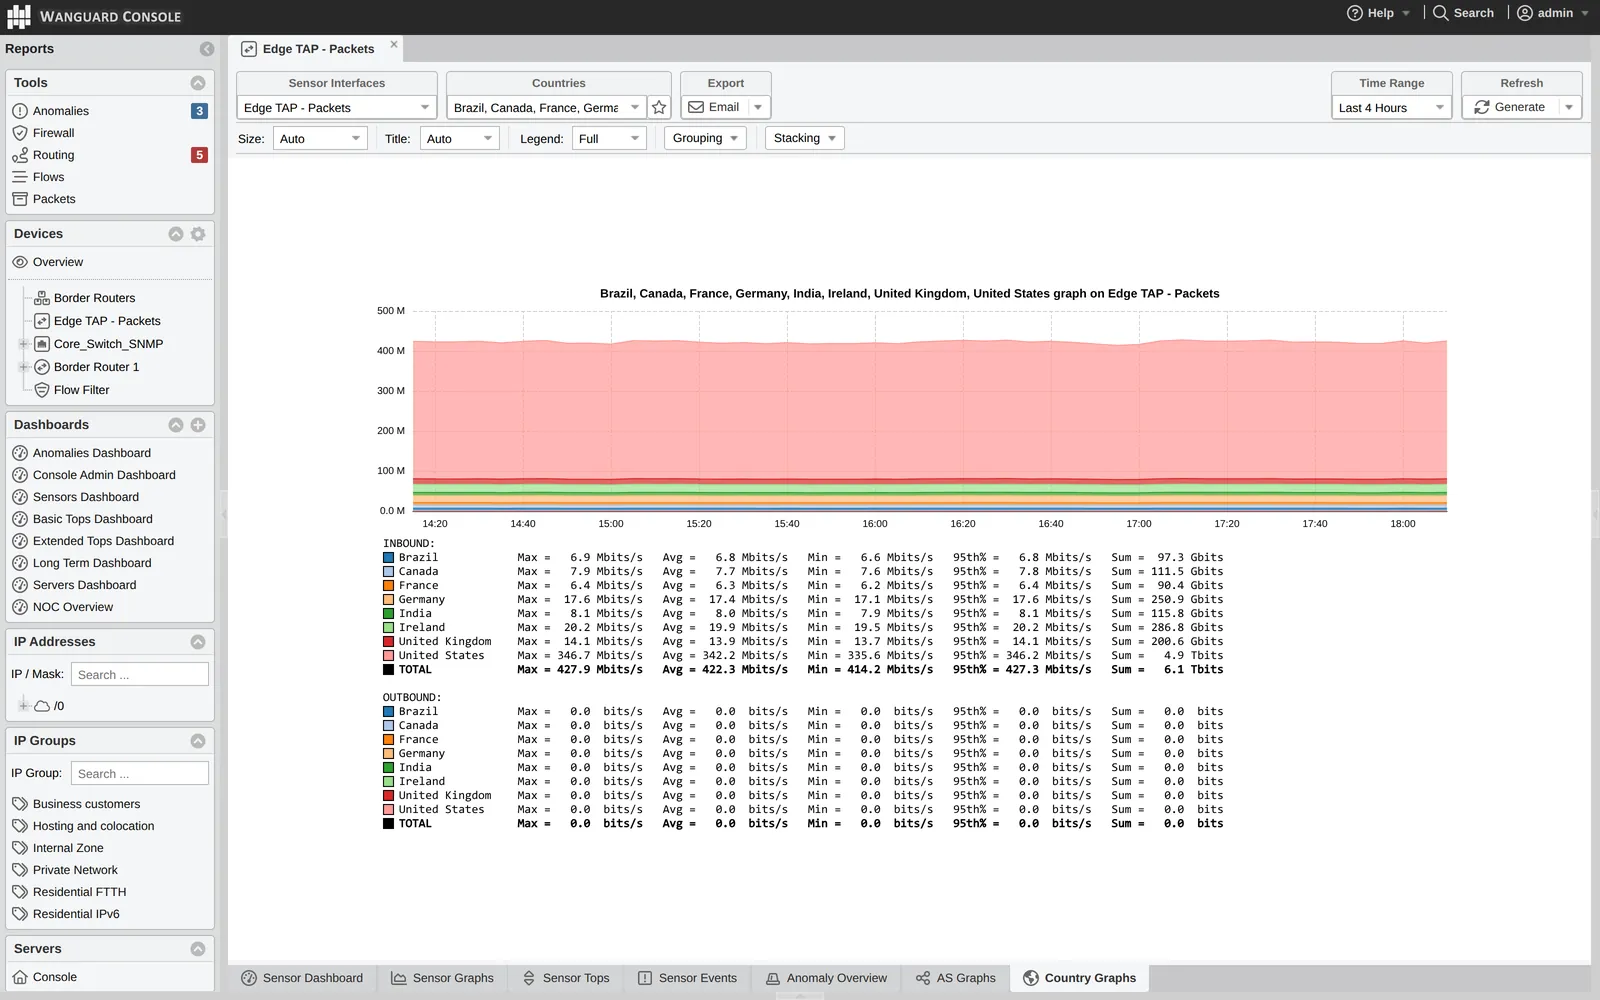
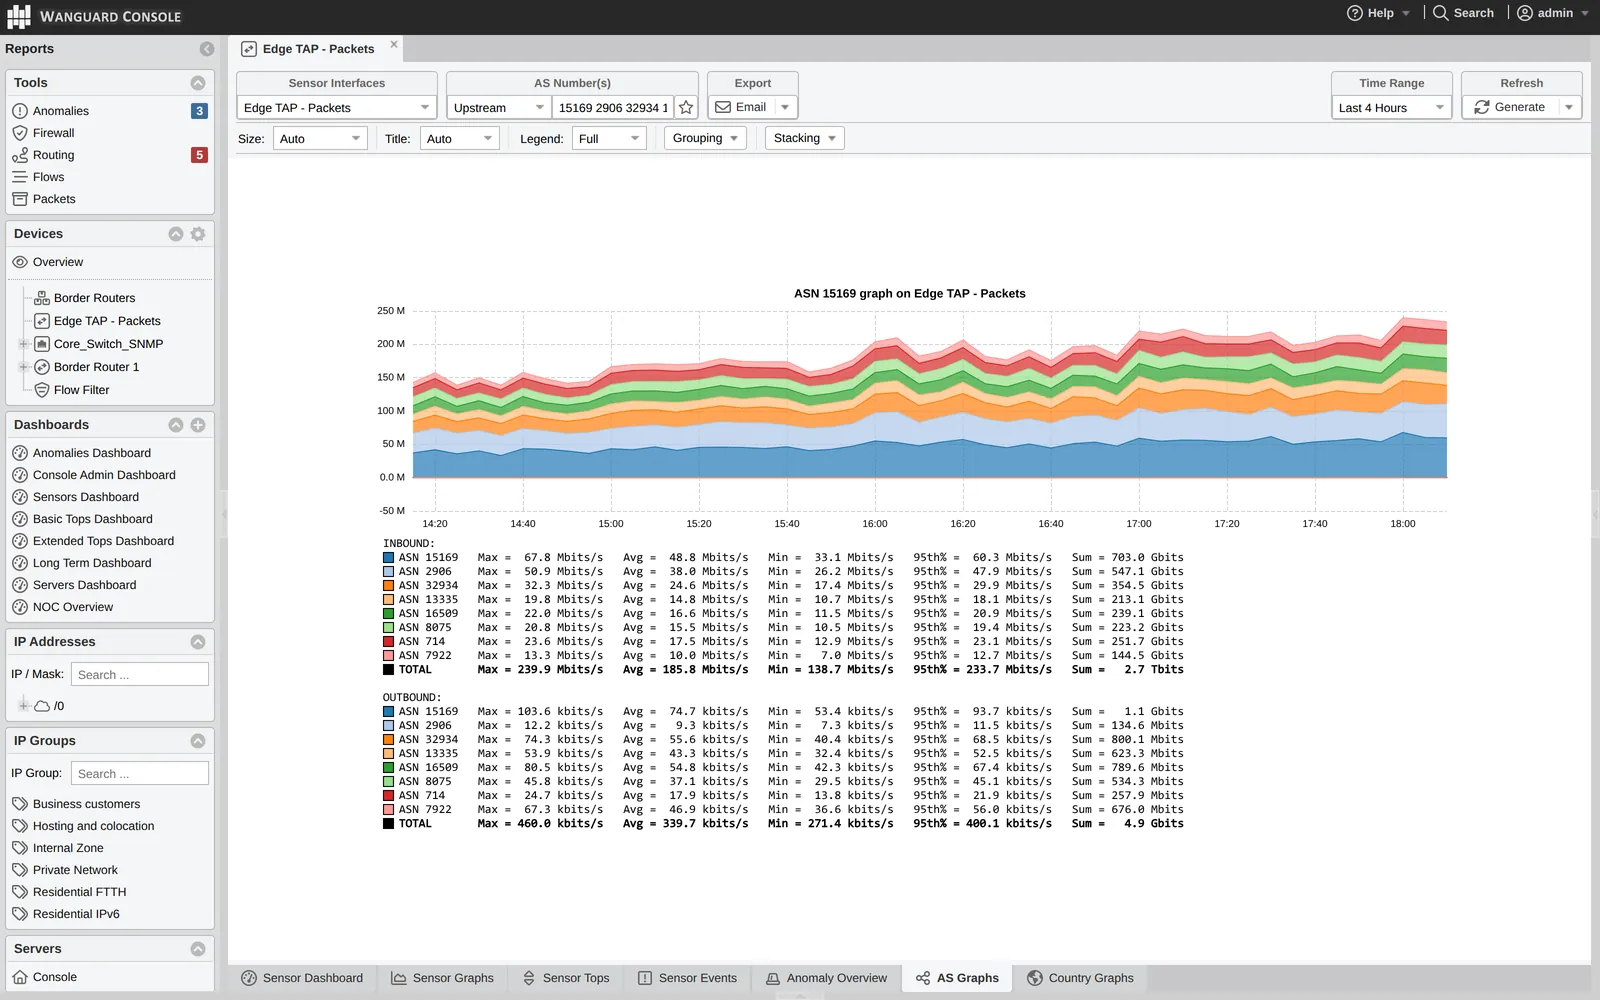
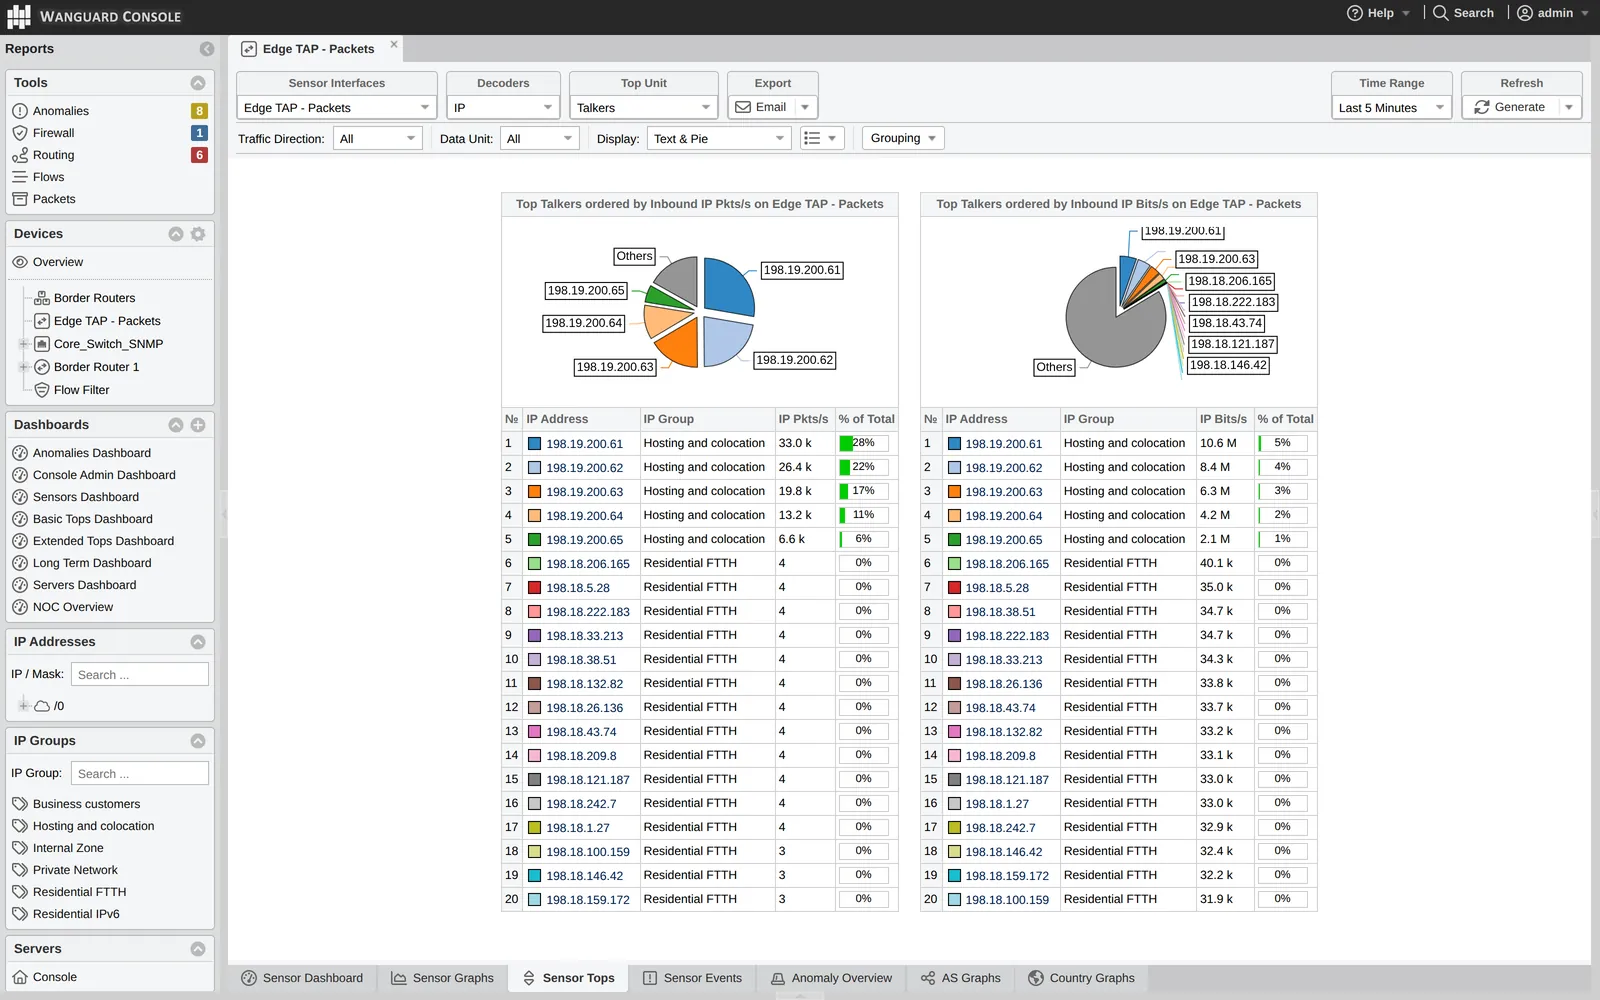
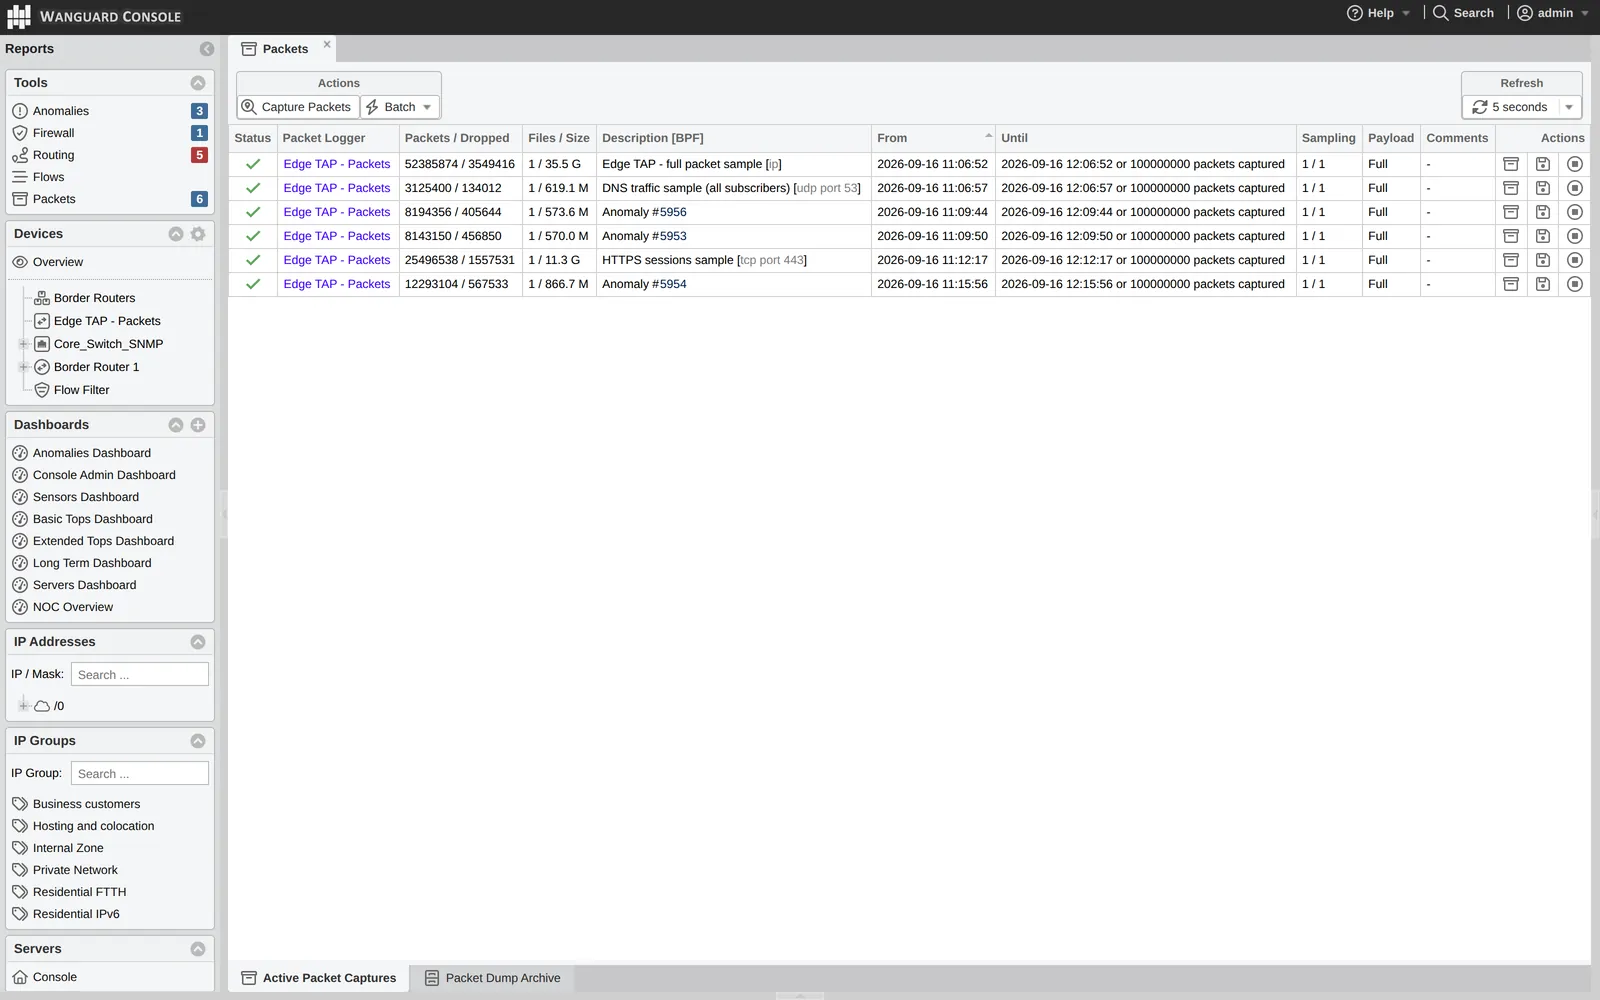
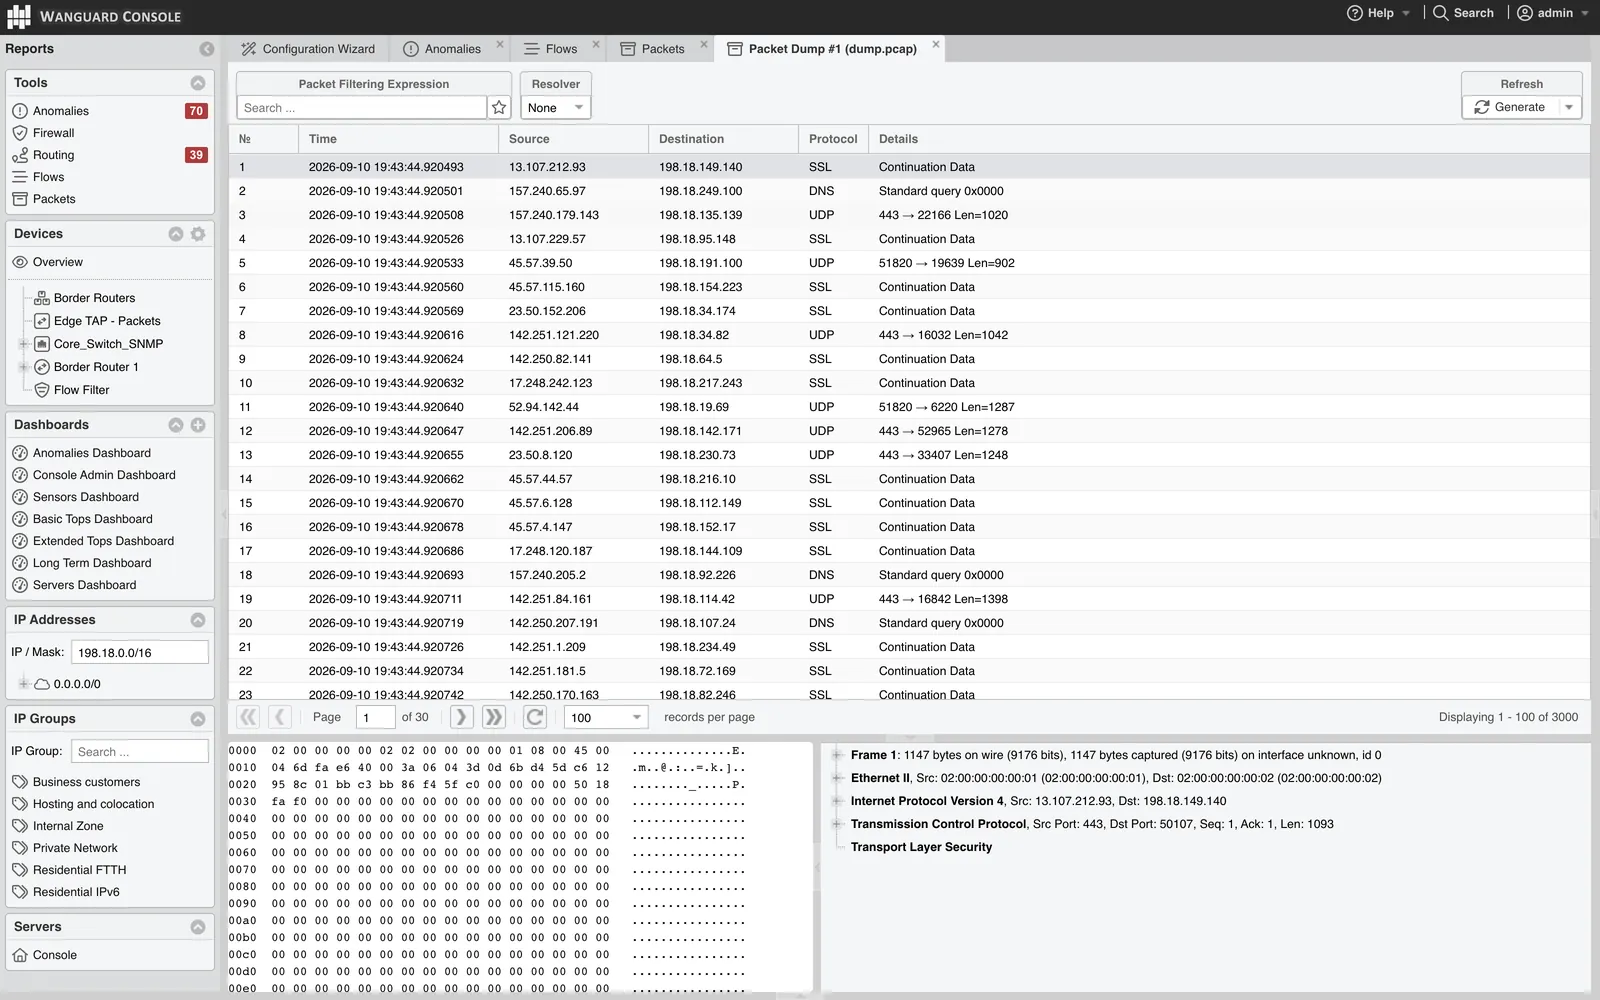
Six screens from a Packet Sensor on a demo network: its traffic graphs, the same traffic by country and by autonomous system, its top talkers, the captures it is running, and one of them opened in the analyzer. Click any of them to enlarge.
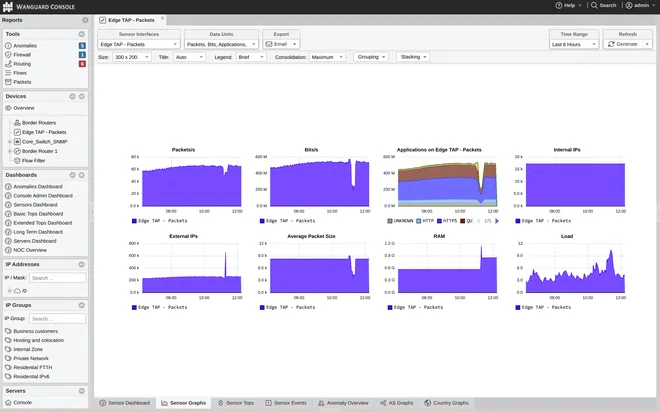 Sensor Graphssix hours on one Packet Sensor in eight small graphs: packets, bits, applications, internal and external IPs, average packet size, RAM and load
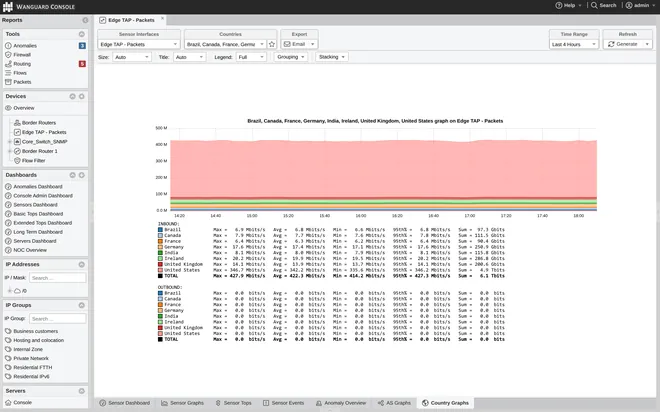 Country Graphsfour hours of inbound traffic from eight countries, stacked, with max, average, 95th percentile and total per country
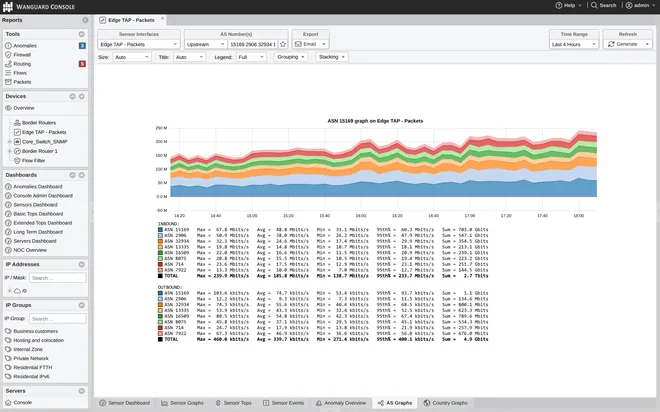 AS Graphsfour hours of traffic with eight upstream autonomous systems, stacked, with max, average, 95th percentile and total per AS
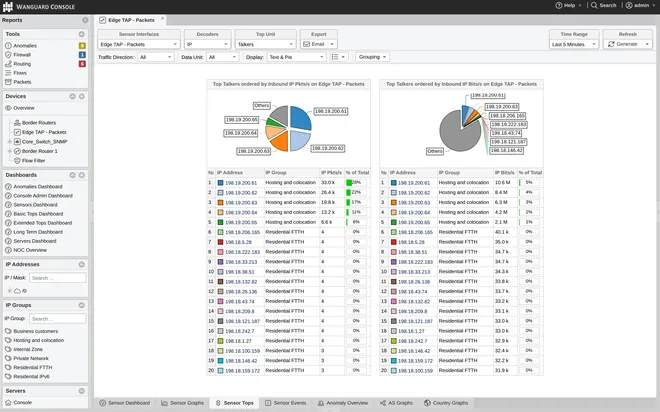 Sensor Topsthe top IP talkers on the Packet Sensor over the last five minutes, by packets and by bits, each as a pie labelled by address and a table
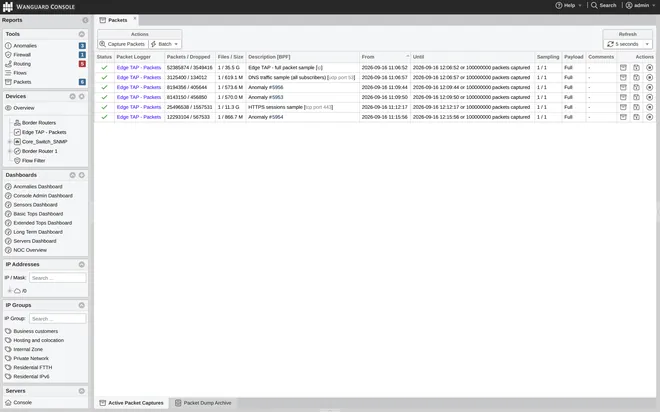 Active Packet Capturessix captures running on a Packet Sensor: three started by hand with BPF filters, three opened automatically by anomalies — packets, drops and file sizes live
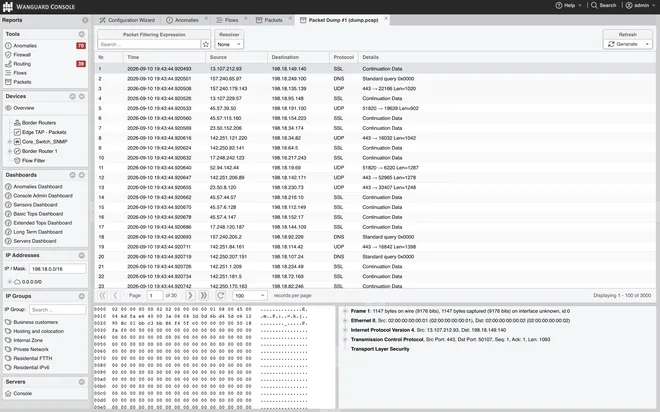 Packet Dump analyzera capture opened in the Console: packet list, protocol tree and hex, like Wireshark in the browser
Every packet, accounted for, checked every second
At its core, the same scalable traffic-correlation engine as the Flow Sensor — monitoring hundreds of thousands of IPv4 and IPv6 addresses and ranges — fed by packets instead of flow records, so it sees everything and sees it first.
See every host and service
Traffic accounting and per-IP, per-subnet or per-IP-group graphs for 50+ decoders — IP, the TCP flag combinations, UDP, ICMP, fragments, QUIC, DNS, NTP, SNMP, SSDP, memcached, GRE, IPv4/IPv6, YouTube, Netflix and your own. Tops and graphs for talkers, external IPs, IP groups, autonomous systems and transit ASes, countries, ports and protocols; graphs as fine as five seconds, history for as many years as you keep.
IP reports in the docs →Detect in one second
With a Wanguard license: DDoS and unknown volumetric DoS; NTP amplification, UDP, ICMP and SMURF floods; SYN floods, TCP/UDP port 0, LOIC, peer-to-peer attacks; scans and worms hitting illegal or unallocated addresses; traffic missing from critical services. Anomaly checks every second — or every five — and a capture of the attacking traffic for the forensics.
How detection works →Respond per endpoint
Activate on-premise mitigation with Wanguard Filter; announce RTBH blackholes with Flowspec (RFC 5575) or null-routing communities; send BGP off-/on-ramp diversion to an on-premise or cloud scrubber; email alerts from dynamic templates; syslog to your SIEM; capture a sample of the traffic; or run your scripts through an API exposing 130+ parameters.
Response actions in the docs →Flows or packets? A Flow Sensor needs no extra hardware and tens of them share a server; the Packet Sensor needs a mirror port, a TAP or a place in the data path, and in return detects in one second with five-second graphs. Many networks run both — choosing a method of traffic monitoring.
Capture, cluster, decapsulate
The Packet Sensor runs as a passive sniffer, or as a transparent bridge or pseudo-Layer-3 device that forwards packets between its ports. It scales by running load-balanced across CPU cores and across servers, and reads the encapsulations carriers actually use.
Packet dumps can be downloaded or viewed online in a Wireshark-like interface, with raw hexadecimal and ASCII for inclusion in regular expressions — for forensic investigation, network-wide situational awareness and troubleshooting.
- libpcap, DPDK, PF_RING (vanilla or ZC) and Netmap for sniffing on > 100 Gbit interfaces with no packet loss
- Clustered mode: Packet Sensor instances load-balanced on different CPU cores or servers; a free Sensor Cluster aggregates them beyond 100 Gbit/s
- Multi-core load balancing with Intel 82599 adapters (X520, X540, HP X560, Silicom PE310G4DBi9-T), PF_RING, Netmap or any DPDK-supported NIC
- MPLS processing in mirror mode; VLAN and double-VLAN (QinQ) tag stripping; PPPoE, GRE and Nokia ip-udp-shim decapsulation
- Traffic validated by IP classes, MAC addresses, VLANs or a BPF expression
- Any number of instances on servers across the network; non-disruptive installation on commodity hardware
Datasheet and minimum server
The datasheet and the two reference servers — 10 and 40 Gbit/s — as the specification sheet has them; the DPDK engine license is needed on top of the Sensor license only when the Sensor runs on DPDK.
Datasheet
| Traffic Capturing Technology: |
|
| Capacity per Sensor Instance: | 100 Gigabit Ethernet, >30 Mpackets/s, unlimited number of connections between IPs |
| DDoS Detection Time: | ≤ 1 second |
| IP Graphing Accuracy: | ≥ 5 seconds |
| Traffic Validation Options: | IP classes, MAC addresses, VLANs, BPF |
Minimum system requirements
| Capacity: | 10 Gbit/s (~14 Mpkts/s) | 40 Gbit/s (~30 Mpkts/s) |
|---|---|---|
| Architecture: | Intel Xeon 64 bit, dedicated server | Intel Xeon 64 bit, dedicated server |
| CPU: | 2.4 GHz 10-core Xeon E5-2640v4 | 2.4 GHz 12-core Xeon E5-2680v4 |
| RAM: | 8 GB DDR4 quad-channel | 16 GB DDR4 quad-channel |
| Network Cards: | 1 x 10 GbE adapter (Intel 82599+ or DPDK supported chipset) 1 x Fast Ethernet for management |
1 x 40 GbE adapter (Intel XL710+ or other DPDK supported chipset) 1 x Fast Ethernet for management |
| Operating System*: | RHEL / Rocky / Alma 9 to 10; Debian 11 to 13; Ubuntu Server 20 to 26 | RHEL / Rocky / Alma 9 to 10; Debian 11 to 13; Ubuntu Server 20 to 26 |
| Disk Space: | 10 GB (including OS) | 10 GB (including OS) |
* Other Linux distributions might work but have not yet been tested.
Full system requirements →DPDK configuration →Sensor licenses, $595 / year →DPDK Engine, $1,410 / year →
Key features and benefits — the complete list
Packet Sniffing (Port Mirroring, Inline Appliances) Sensor for Wanguard and Wansight
The Packet Sensor component of Wanguard and Wansight is a packet sniffer that inspects IP packets and generates detailed traffic analytics. At its core, it contains a highly scalable traffic correlation engine capable of continuously monitoring hundreds of thousands of IP addresses. Sophisticated statistical algorithms integrate traffic data to build an accurate and detailed picture of real-time and historical traffic flows across the network.
- Provides traffic accounting reports and per-IP, subnet or IP group graphs for each of the following traffic decoders (classes): IP, TCP, TCP+SYN, TCP+RST, TCP+ACK, TCP+SYNACK, TCP+ACK+PSH, TCP+RST+FIN, TCP+FIN, TCP+ALL, TCP-NULL, TCP0, UDP, UDP0, UDP-QUIC, ICMP, OTHER, INVALID, FRAGMENT, QUIC, MEMCACHED, HTTP, HTTPS, WWW, MAIL, DNS, SIP, SSH, NTP, SNMP, RDP, SSDP, LDAP, CLDAP, CHARGEN, SLP, NETBIOS, NBNS, IPSEC, GRE, ARMS, COAP, MSSQLRS, STUN, WSDD, RIPV1, MDNS, RPCBIND, IPV4, IPV6, FACEBOOK, YOUTUBE, NETFLIX, HULU — plus custom decoders
- Generates tops and graphs for talkers, external IPs, IP groups, autonomous systems (GeoIP based), transit autonomous systems (based on BGP MTR files), countries, TCP ports, UDP ports, IP protocols and more
- Users can save packet dumps for forensic investigation, network-wide situational awareness and to aid network troubleshooting — downloaded or viewed online in a Wireshark-like interface, which displays packet captures in hexadecimal raw and ASCII data for inclusion in regular expressions
- Using libpcap, DPDK, PF_RING (vanilla or ZC) or Netmap, it sniffs >100 Gbit interfaces with no packet losses
- Supports MPLS processing in mirror mode, VLAN and double-VLAN tag stripping, PPPoE, GRE and Nokia ip-udp-shim decapsulation — while acting as a passive sniffer, or as a transparent bridge or (pseudo) Layer 3 device forwarding packets between ports
- Per-endpoint flexible threat reaction options with a Wanguard license: on-premise mitigation, remotely-triggered BGP blackhole announcements, off-/on-ramp diversion to on-premise / on-cloud mitigation services, email alerts with user-defined dynamic templates, custom Syslog messages to remote log servers or SIEM systems, traffic samples for forensics, and custom scripts executing with access to an easy-to-use API exposing 130+ internal parameters to extend the built-in capabilities
- Short-term accuracy of bandwidth graphs and anomaly checks of 5 seconds or 1 second; detects bandwidth-related traffic anomalies — from Distributed Denial of Service (DDoS) attacks and generic UDP floods to scans and worms sending traffic to illegal or unallocated addresses and missing traffic to/from critical services — when used with a Wanguard license; long-term accuracy of any number of years
- A completely scalable IP traffic analysis engine, monitoring hundreds of thousands of IPv4 and IPv6 addresses and ranges in real time — clustered mode load-balances any number of Packet Sensors across CPU cores and servers, management and reporting through the advanced web-based Console with a unified presentation, easy and non-disruptive installation on commodity hardware
The rest of Wanguard
Packet Sensor is one of four components; every one reports to the same Console. Wansight runs the same Sensor without detection and mitigation — and becomes Wanguard with a license key.
Console
The workbench
Web UI, reports, dashboards, users and the API — the brain of the deployment.
Multi-tenant, with 40+ dashboard widgets, scoped views for customers, white-label login for MSSPs, PDF and Excel exports, 10 themes including a dark mode.
- License
- free, unlimited users
- Auth
- SAML 2.0, LDAP/AD, RADIUS
- Automation
- REST API, CLI, scripts
Flow Sensor
Listens to routers
Collects and analyzes the flows your routers already export.
NetFlow v5/v7/v9, jFlow, cflowd, NetStream, sFlow v4/v5 and IPFIX; one instance per exporter, tens of instances per server; an optional flow collector with interactive flow graphs.
- Per instance
- 1 exporter, tens of 10/40/100 GbE ports
- Detection
- ≤ export time + 5 s
- License
- $595 / year
Filter
Scrubs the attack
Turns an anomaly into precise filtering rules, then applies them.
Packet Filter inspects diverted or in-line packets, with deep packet inspection for payload patterns; Flow Filter derives the same rules from any Flow Sensor's flows on minimal hardware. Both apply them anywhere: local Netfilter, in-NIC filters (Intel 82599, Chelsio T5+, any DPDK Flow API card), BGP Flowspec routers or third-party appliances.
- Packet Filter
- 10–40 Gbps per server, rules < 1 s
- Flow Filter
- 1 Tbps+ via Flowspec, rules 5–10 s
- License
- $995 / year
Try the full product on your own hardware
Every feature, any number of servers, 30 days — by requesting a free evaluation license. Our engineers help you set it up.
Debian 11–13Ubuntu 20–26RHEL 9–10RockyAlmaLinux
1
Request a key
Fill in the trial form. We review it and email download links, documentation and a 30-day license within 24 hours.
2
Install on a spare Linux server
Any 64-bit Intel/AMD box or VM. Packages install under /opt in minutes; size the hardware with the system requirements.
3
Run it for real, then buy
Ask us anything during the trial. When it earns its keep, buy licenses in the online store — the trial installation carries on with the new key.
Already running Wanguard?
Wanguard 9.0 is out (23 July 2026). Upgrading from 8.x? Read the release notes first.